 Princeton IT Services

Agent activity log
Every prompt, tool call, answer and cost, per agent and per user.
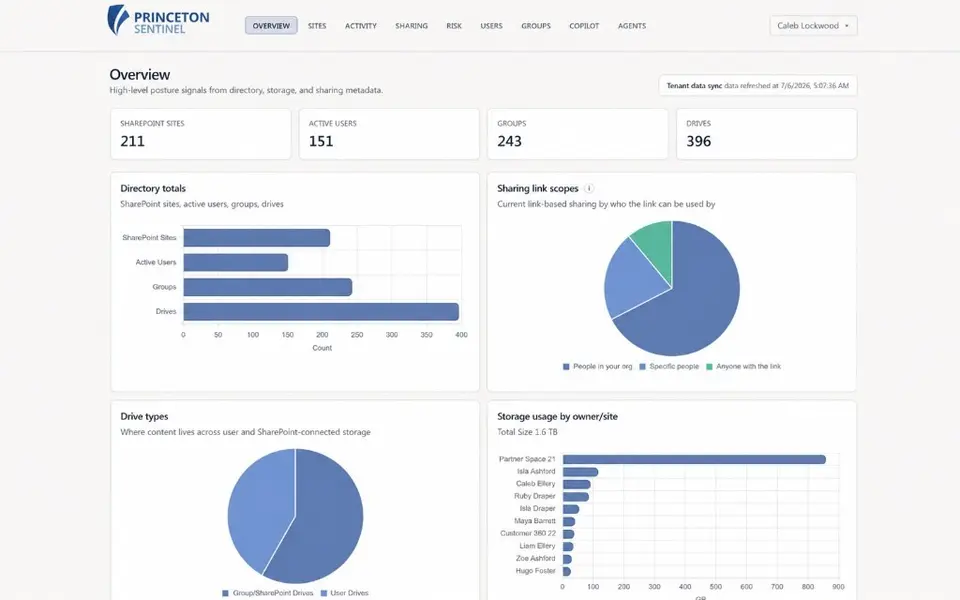
Sentinel gives security and IT leaders one view of Copilot and Copilot Studio agents in Microsoft 365: what they are asked, what they touch, how risky each one is, and where data is overshared.
Features
Every prompt, tool call, answer and cost, per agent and per user.

A rules layer plus a locally hosted classifier checks each prompt, with no per-call fees.

Each agent scored on how it is configured and on what it actually does.

Files shared too widely and accounts that should have been removed.

One page for leadership, with the trend over time.

Purview audit data collected and kept for review.
How it works
Approve a Microsoft Entra app registration with read-only permissions.
Sentinel gathers Purview audit events, Microsoft Graph data and agent activity.
Dashboards, alerts and a monthly review of what changed and what to fix.
Case studies
Client names are withheld. We are happy to share details on a call.
Every prompt screened
Any industry on Microsoft 365
Sentinel watches Copilot and Copilot Studio agents in a Microsoft 365 tenant. It logs prompts and tool calls, scores each agent's risk, flags oversharing and stale access, and screens prompts for injection attempts with a classifier that runs locally at no per-call cost.
 Every agent prompt screenedRuns inside the customer's own Azure tenant
A 30-minute demo on a sample tenant, then a read-only trial in yours.
A few lines is enough. The engineers who do this work will reply within one business day.
Or email it.services@princetonits.com or call +1 (212) 507-9350.