

Data Poisoning in AI: Prevention, Defense & Governance
Data Poisoning in AI: Defending, Preventing, and Governing Multi-Agent Systems Security
Most enterprise conversations around AI security threats still stop at awareness. Teams understand that data poisoning in AI is real, that retrieval indexes and agent memory are exposed, and that attacker economics are shifting.
What leadership teams, CISOs, and auditors now want is clarity on what actually needs to be built, monitored, and owned to secure multi-agent systems security in production environments.
The reality is simple: no single control can stop AI data poisoning attacks. Attack surfaces are too broad, and LLM vulnerabilities are too dynamic. The only approach that works is layered—combining prevention, runtime defense, and strong AI governance frameworks backed by industry standards.
Defense vs Prevention in AI Security
Two complementary approaches address machine learning data poisoning:
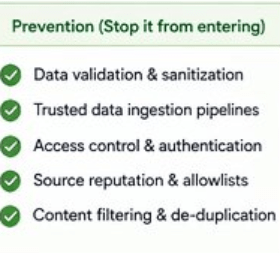
- Prevention: Stops poisoned data from entering systems
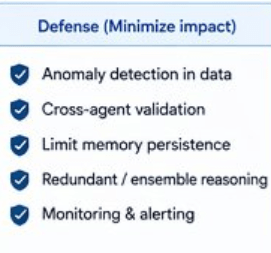
- Defense: Limits impact when prevention fails
Mature organizations invest in both. Relying only on prevention is risky because attackers need minimal effort to inject malicious data, while defenders must validate large datasets.
Prevention Controls for AI Model Poisoning
Prevention focuses on securing the data layer—the most critical surface in AI model poisoning.
Key controls include:
- Data validation and sanitization before ingestion
- Trusted pipelines with hashing and lineage tracking
- Access control to restrict who modifies datasets
- Source reputation and allowlists
- Content filtering and deduplication
These controls reduce exposure but don’t eliminate risk. Sophisticated attackers can still manipulate trusted sources or generate highly realistic poisoned data.
Runtime Defense Against AI Data Poisoning Attacks
Defense mechanisms operate during execution and are essential for modern AI risk management.
Effective strategies include:
- Anomaly detection in AI systems to identify unusual patterns
- Cross-agent validation to reduce malicious execution
- Limiting memory persistence to reduce long-term impact
- Trust-aware retrieval and temporal decay
- Ensemble reasoning across multiple agents
- Continuous monitoring with telemetry tracking
Telemetry plays a critical role. In many real-world incidents, including agent-based attacks, the compromise is only visible when analyzing system-wide behavior—not individual prompts.
Governance: The Backbone of AI Security Frameworks
Strong AI governance frameworks connect prevention and defense into a measurable system.
Industry standards shaping AI security frameworks include:
- OWASP Top 10 for LLM Applications
- MITRE ATLAS framework
- NIST AI Risk Management Framework
These standards translate into six operational control areas:
- Data Lineage
Tracks data origin and transformations—critical for preventing data poisoning in AI.
- Policy Enforcement
Defines what agents can access, ensuring controlled execution.
- Auditability
Maintains logs for investigation and compliance.
- Human-in-the-Loop Security
Adds checkpoints for high-risk actions—one of the most reliable safeguards.
- Continuous Monitoring
Detects runtime threats missed by static filters.
- Risk and Compliance Management
Aligns systems with regulatory and enterprise requirements.

A Practical Approach to Multi-Agent AI Security
To strengthen multi-agent systems security, organizations should:
- Inventory all AI components (agents, tools, memory, retrievers)
- Map risks to frameworks like MITRE ATLAS and OWASP
- Implement telemetry across all layers
Research shows that nearly 70% of AI security controls already exist within traditional security systems. The gap lies in mapping and adapting them to AI-specific threats.
Closing the Loop: AI Security is a Data Problem
Securing AI systems is not just about models—it’s about controlling data and behavior.
- Prevention reduces what enters the system
- Defense limits damage during attacks
- Governance ensures accountability and continuous improvement
As adversarial machine learning attacks evolve, organizations must assume that poisoning will eventually occur. The focus should shift to detection, response, and recovery.
In modern AI environments, especially those using agents, the data layer is the security layer.
Categories
- Accessibility solutions (3)
- AI / LLMOps (AI Observability & Monitoring) (3)
- AI & Automation (17)
- AI Governance & Responsible AI (4)
- AI Security (4)
- Android (17)
- Angular JS (1)
- API & Integration / Developer Tools (1)
- Apple (3)
- Artificial Intelligence (1)
- Artificial Intelligence (AI) (16)
- AV & Collaboration Technology (2)
- AWS Cloud Computing (2)
- AWS DMS (6)
- AWS RDS (12)
- Azure (3)
- BI & ANALYTICS (16)
- Cloud Computing & AI (5)
- Cloud Identity & Directory Services (1)
- Cloud Migration (12)
- Cloud Security & Identity Management (3)
- Company News (5)
- Continuous integration and continuous deployment (2)
- Cybersecurity (7)
- Data Analytics (12)
- Data Engineering (8)
- Data Governance & Compliance (6)
- Data Management (5)
- Data Migration (9)
- Data Quality (1)
- Data Quality & Data Governance (1)
- DBA (10)
- DevOps (1)
- Email Security (1)
- Endpoint Management / Device Management (1)
- Enterprise AI / AI Governance (1)
- Enterprise AI / AI Implementation Best Practices (1)
- Enterprise AI & Intelligent Automation (2)
- Enterprise Mobility & Security (1)
- Enterprise Software Integration / Backend Development (1)
- Enterprise Technology (1)
- Enterprise UX/UI Design (1)
- Goldengate (19)
- Google (2)
- Hadoop (3)
- HPNA (1)
- Ios (10)
- ios 10 (2)
- iPad (3)
- iPhone (3)
- Licensing (7)
- Linux (13)
- Machine Learning Solutions (1)
- Marketing Technology (1)
- Microsoft 365 (1)
- Microsoft 365 Development / APIs (1)
- Microsoft 365 Security & Compliance (4)
- Microsoft Configuration Manager (SCCM / MECM) (1)
- Microsoft Dynamics 365 (4)
- Microsoft Marketplace (1)
- Microsoft Office (5)
- Microsoft Purview (3)
- Microsoft SharePoint & Security (1)
- Microsoft Teams / Collaboration Tools (1)
- Microsoft Teams Security & Compliance (2)
- Mobile (2)
- Network Automation (5)
- Network Security Services (1)
- News (21)
- Operating System (1)
- Oracle (37)
- oracle consulting (3)
- PostgreSQL (1)
- Quantum Computing (1)
- Quickbooks (1)
- SEO (1)
- Software Development (33)
- Systems Automation (2)
- Tech (3)
- Technology (51)
- UI (13)
- Uncategorized (8)
- UX (9)
- VSTO (1)
- Web Development (1)
- Windows (9)
- wordpress (1)