

AI Data Poisoning: RAG, LLM & Multi-Agent Security
Data Poisoning in AI: Attack Surfaces & Attack Types in Multi-Agent Systems
The Slack AI data exfiltration incident (August 2024), PoisonedRAG research presented at USENIX Security 2025, and Unit 42’s agent session smuggling findings all point to a critical shift in AI security risks. These cases highlight how data poisoning in AI systems is no longer limited to model training—it now impacts real-time decision-making inside multi-agent environments.
Today, the security boundary has moved beyond traditional infrastructure. It now exists inside vector databases, retrieval systems (RAG), agent memory, and tool integrations—areas that most enterprise security frameworks are not fully equipped to monitor.
Understanding the Attack Surface in AI Systems
In modern enterprise environments, especially those using multi-agent systems (MAS), AI attack surfaces have expanded significantly.
The diagram below maps these surfaces against a typical orchestrator-plus-agents architecture

Data poisoning can enter the system through six key points:
- Data Sources (Entry Point for Prompt Injection Attacks)
This is where external and internal data enters the system—web content, vendor documents, APIs, and user uploads.
It is also the primary layer for prompt injection attacks, where malicious instructions are hidden within legitimate-looking content.
A well-known example is the Slack AI incident, where poisoned inputs triggered unintended data exposure.
- Retrieval Corpus (RAG & Vector Database Security Risks)
Retrieval-Augmented Generation (RAG) systems rely on vector databases to fetch relevant information.
Research like PoisonedRAG shows that inserting just a few malicious entries can manipulate outputs—even in massive datasets.
This highlights a major concern in vector database security:
- Attackers need minimal effort
- Defenders must secure massive datasets
- Agent Memory (Persistent AI Vulnerabilities)
Agent memory stores information across sessions, making it a high-risk component.
Attacks like AgentPoison and MINJA demonstrate how agent memory poisoning can:
- Persist over time
- Influence future outputs
- Bypass traditional safeguards
Unlike prompt injection, this is not temporary—it becomes a long-term compromise.
- External Tools & APIs (AI Supply Chain Attacks)
Agents frequently interact with external tools, APIs, and MCP servers.
This creates multiple risks:
- Malicious tool descriptions
- API response manipulation
- Tool shadowing attacks
These fall under broader AI supply chain attacks, where trust in external integrations becomes a vulnerability.
- Model Updates & Training Data (Machine Learning Data Poisoning)
One of the most critical layers is the training pipeline.
Studies show:
- As few as 250 poisoned samples can backdoor large models
- Even 0.001% corrupted data can influence outcomes
This reinforces the growing threat of machine learning data poisoning in enterprise AI.
- Feedback Loops (AI Feedback Loop Attacks)
User feedback, ratings, and reinforcement learning signals can also be exploited.
Research shows that malicious inputs can:
- Spread across agents
- Trigger AI agent privilege escalation
- Create self-propagating attacks
Types of Data Poisoning Attacks in AI
The six surfaces describe where poisoning enters the system; four functional types describe what the attacker is trying to achieve. Any surface can be exploited to produce any of these effects — the surfaces and types are independent dimensions.
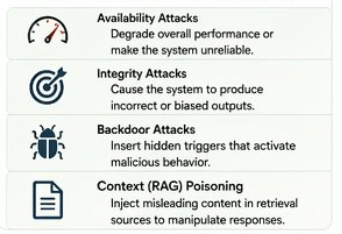
- Availability Attacks
These degrade system performance or cause failures.
- Example:
- Models generating unusable or irrelevant outputs
- Integrity Attacks
These manipulate outputs for specific inputs.
Example:
- Biased or incorrect responses in critical domains like healthcare
- Backdoor Attacks
These introduce hidden triggers that activate malicious behavior.
- The model behaves normally
- But fails when a trigger is present
- Context (RAG) Poisoning
This targets retrieval systems instead of the model itself.
- Injected content influences responses at runtime
- No need to modify the model
What This Means for Enterprise AI Security
The combination of these attack surfaces and attack types reveals three major realities:
- Traditional Security Models Are No Longer Enough
Security must now extend to:
- Vector databases
- Agent memory
- Tool ecosystems
- Attackers Have an Economic Advantage
A handful of malicious inputs can compromise systems built on millions of data points.
- Data is Now Executable
In AI systems, data is no longer passive—it acts as instructions.
This is the core reason why AI data poisoning attacks are so dangerous.
Conclusion: Securing Multi-Agent Systems Against Data Poisoning
The biggest takeaway is clear:
The model itself is not the main risk—the ecosystem around it is.
To protect against data poisoning in AI, organizations must:
- Secure data pipelines before ingestion
- Monitor RAG systems and vector databases
- Validate external tools and APIs
- Implement memory and feedback safeguards
As AI adoption grows, multi-agent system security will become a top priority for enterprises.
Categories
- Accessibility solutions (3)
- AI / LLMOps (AI Observability & Monitoring) (3)
- AI & Automation (17)
- AI Governance & Responsible AI (4)
- AI Security (4)
- Android (17)
- Angular JS (1)
- API & Integration / Developer Tools (1)
- Apple (3)
- Artificial Intelligence (1)
- Artificial Intelligence (AI) (16)
- AV & Collaboration Technology (2)
- AWS Cloud Computing (2)
- AWS DMS (6)
- AWS RDS (12)
- Azure (3)
- BI & ANALYTICS (16)
- Cloud Computing & AI (5)
- Cloud Identity & Directory Services (1)
- Cloud Migration (12)
- Cloud Security & Identity Management (3)
- Company News (5)
- Continuous integration and continuous deployment (2)
- Cybersecurity (7)
- Data Analytics (12)
- Data Engineering (8)
- Data Governance & Compliance (6)
- Data Management (5)
- Data Migration (9)
- Data Quality (1)
- Data Quality & Data Governance (1)
- DBA (10)
- DevOps (1)
- Email Security (1)
- Endpoint Management / Device Management (1)
- Enterprise AI / AI Governance (1)
- Enterprise AI / AI Implementation Best Practices (1)
- Enterprise AI & Intelligent Automation (2)
- Enterprise Mobility & Security (1)
- Enterprise Software Integration / Backend Development (1)
- Enterprise Technology (1)
- Enterprise UX/UI Design (1)
- Goldengate (19)
- Google (2)
- Hadoop (3)
- HPNA (1)
- Ios (10)
- ios 10 (2)
- iPad (3)
- iPhone (3)
- Licensing (7)
- Linux (13)
- Machine Learning Solutions (1)
- Marketing Technology (1)
- Microsoft 365 (1)
- Microsoft 365 Development / APIs (1)
- Microsoft 365 Security & Compliance (4)
- Microsoft Configuration Manager (SCCM / MECM) (1)
- Microsoft Dynamics 365 (4)
- Microsoft Marketplace (1)
- Microsoft Office (5)
- Microsoft Purview (3)
- Microsoft SharePoint & Security (1)
- Microsoft Teams / Collaboration Tools (1)
- Microsoft Teams Security & Compliance (2)
- Mobile (2)
- Network Automation (5)
- Network Security Services (1)
- News (21)
- Operating System (1)
- Oracle (37)
- oracle consulting (3)
- PostgreSQL (1)
- Quantum Computing (1)
- Quickbooks (1)
- SEO (1)
- Software Development (33)
- Systems Automation (2)
- Tech (3)
- Technology (51)
- UI (13)
- Uncategorized (8)
- UX (9)
- VSTO (1)
- Web Development (1)
- Windows (9)
- wordpress (1)