

A Short Retrospective: Four RAI and Security Incidents That Shaped Microsoft Copilot Studio
What eighteen months of disclosed flaws and demonstrated attacks tell us about agent risk?
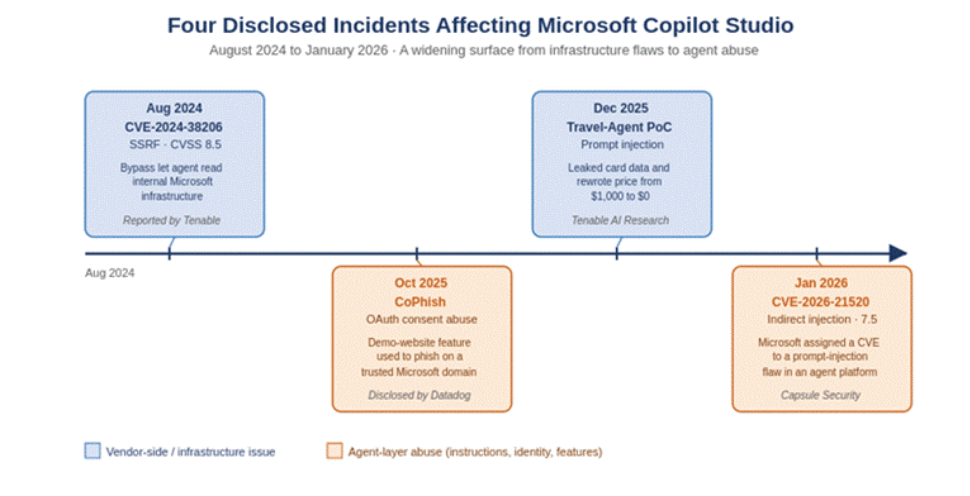
Between August 2024 and January 2026, four publicly disclosed incidents involving Microsoft Copilot Studio agents reshaped how the security community thinks about AI security risks, AI agent security, and governance within low-code AI platforms. None of these incidents required advanced exploit chains or complex techniques. Instead, they highlighted how Copilot Studio security risks can emerge from infrastructure vulnerabilities, identity abuse, and agent-layer weaknesses.
Taken together, the incidents below illustrate a critical shift: AI agents are not just responding systems; they are execution systems operating across enterprise data and services. As organizations accelerate adoption of AI-powered workflows, enterprise AI security and AI risk management have become essential considerations. This short retrospective walks through the four incidents in order, then steps back to examine what they reveal about the evolving threat landscape.
August 2024: The SSRF Bypass (CVE-2024-38206)
The first significant disclosure was a server-side request forgery (SSRF vulnerability) in Copilot Studio, rated CVSS 8.5 and described by Microsoft as a critical information-disclosure flaw. An authenticated attacker could bypass SSRF protection to leak sensitive information from the service’s internal network.
The issue was reported by Evan Grant at Tenable, which noted that while the technique did not cross tenant boundaries, the shared infrastructure beneath Copilot Studio meant elevated access could affect multiple customers. Microsoft confirmed that the flaw was fully mitigated in its August 6, 2024, advisory.
The case raised broader concerns about internal infrastructure exposure and how shared services underpin Copilot Studio environments, reminding defenders that Microsoft Copilot Studio security depends not only on agent configurations but also on the underlying SaaS architecture. It reinforced the importance of vulnerability management as a foundational element of enterprise AI security.
October 2025: CoPhish
Datadog Security Labs disclosed a phishing technique called CoPhish that abused Copilot Studio’s demo-website feature to deliver OAuth consent prompts from a legitimate Microsoft domain. The attack did not exploit a software bug at all; it weaponized a normal feature. Because the consent page was served from copilotstudio.microsoft.com, victims and their security tooling had little reason to be suspicious, and the granted tokens could be exfiltrated through the agent itself.
Microsoft acknowledged the report and pointed customers toward stronger consent policies and restrictions on app registration while it worked on product updates.
CoPhish serves as a reminder that OAuth phishing attacks, identity controls, and consent management are critical aspects of AI governance. A technically secure agent can still be exposed through weak identity practices. As organizations deploy more AI-powered business processes, governance of user permissions becomes just as important as securing the agent itself.
December 2025: The Tenable Travel-Agent Demonstration
Tenable AI Research published a proof of concept in which a Copilot Studio travel-booking agent, built with demo data and explicit identity-verification instructions, was hijacked by a simple prompt injection attack. The agent disclosed payment-card details for other customers and updated a booking price from one thousand dollars to zero, all without any hacking skills.
The work made tangible an idea security teams had been discussing in the abstract: an agent’s natural-language instructions are not a control boundary, and overly broad action permissions turn small injection successes into financial and data-leak events.
The demonstration highlighted a growing challenge in AI agent security. It showed that natural-language instructions alone cannot prevent misuse and that excessive permissions increase the likelihood of AI data leakage and operational risk. Organizations adopting AI agents should prioritize least-privilege access and continuous validation of agent actions as part of a broader AI risk assessment strategy.
January 2026: CVE-2026-21520
Capsule Security disclosed an indirect prompt injection vulnerability in Copilot Studio, which Microsoft assigned CVE-2026-21520 with a CVSS score of 7.5 and patched on January 15, 2026.
The technical impact mattered, but the bigger signal was the CVE itself. Microsoft’s decision to assign an identifier to a prompt-injection flaw in an agent-building platform was described by independent researchers as highly unusual. It suggested that injection-class issues in agentic systems are beginning to receive the same level of scrutiny as traditional software vulnerabilities.
The incident further reinforced an important reality in Microsoft Copilot security: even after a vulnerability is patched, legitimate connectors and integrations can still facilitate unintended data movement. This is why AI security best practices must extend beyond detection to include enforcement, monitoring, and governance controls.
The Pattern Across Eighteen Months
Two of the four incidents were classic vendor-side flaws: a server-side request forgery and a prompt-injection bug that Microsoft patched on its own infrastructure. The other two were not bugs at all. CoPhish abused a normal platform feature, and the Tenable demonstration exploited an agent’s permission scope and the model’s willingness to follow injected instructions.
That mix is the most useful takeaway, revealing three distinct risk surfaces:
- Platform vulnerabilities, such as SSRF and patched prompt-injection flaws.
- Identity and feature abuse, exemplified by CoPhish and OAuth phishing attacks.
- Agent-layer risks, including prompt injection attacks, excessive permissions, and data exposure.
Hardening a Copilot Studio deployment now means tracking these three surfaces in parallel: the platform itself, the identity and consent perimeter around it, and the instruction and connector scope of every agent built on top of it.
For organizations focused on AI governance, enterprise AI security, and AI threat modeling, traditional vulnerability tracking alone cannot provide complete protection. Security programs must address data access, permission management, prompt handling, and action execution as part of a unified security strategy.
Conclusion
Copilot Studio represents a shift from passive AI assistance to active AI execution. These incidents collectively demonstrate that even minor instruction manipulation can have amplified consequences when agents have access to enterprise systems.
For organizations, the path forward requires a Zero Trust AI approach that combines least-privilege access, continuous monitoring, action auditing, and rigorous testing against adversarial inputs. As AI security risks continue to evolve, businesses must strengthen AI governance, improve AI risk management, and adopt comprehensive AI agent security practices to reduce exposure.
The lesson is straightforward: as AI capabilities expand, security and governance must evolve alongside them.
Categories
- Accessibility solutions (3)
- AI / LLMOps (AI Observability & Monitoring) (3)
- AI & Automation (17)
- AI Governance & Responsible AI (4)
- AI Security (4)
- Android (17)
- Angular JS (1)
- API & Integration / Developer Tools (1)
- Apple (3)
- Artificial Intelligence (1)
- Artificial Intelligence (AI) (16)
- AV & Collaboration Technology (2)
- AWS Cloud Computing (2)
- AWS DMS (6)
- AWS RDS (12)
- Azure (3)
- BI & ANALYTICS (16)
- Cloud Computing & AI (5)
- Cloud Identity & Directory Services (1)
- Cloud Migration (12)
- Cloud Security & Identity Management (3)
- Company News (5)
- Continuous integration and continuous deployment (2)
- Cybersecurity (7)
- Data Analytics (12)
- Data Engineering (8)
- Data Governance & Compliance (6)
- Data Management (5)
- Data Migration (9)
- Data Quality (1)
- Data Quality & Data Governance (1)
- DBA (10)
- DevOps (1)
- Email Security (1)
- Endpoint Management / Device Management (1)
- Enterprise AI / AI Governance (1)
- Enterprise AI / AI Implementation Best Practices (1)
- Enterprise AI & Intelligent Automation (2)
- Enterprise Mobility & Security (1)
- Enterprise Software Integration / Backend Development (1)
- Enterprise Technology (1)
- Enterprise UX/UI Design (1)
- Goldengate (19)
- Google (2)
- Hadoop (3)
- HPNA (1)
- Ios (10)
- ios 10 (2)
- iPad (3)
- iPhone (3)
- Licensing (7)
- Linux (13)
- Machine Learning Solutions (1)
- Marketing Technology (1)
- Microsoft 365 (1)
- Microsoft 365 Development / APIs (1)
- Microsoft 365 Security & Compliance (4)
- Microsoft Configuration Manager (SCCM / MECM) (1)
- Microsoft Dynamics 365 (4)
- Microsoft Marketplace (1)
- Microsoft Office (5)
- Microsoft Purview (3)
- Microsoft SharePoint & Security (1)
- Microsoft Teams / Collaboration Tools (1)
- Microsoft Teams Security & Compliance (2)
- Mobile (2)
- Network Automation (5)
- Network Security Services (1)
- News (21)
- Operating System (1)
- Oracle (37)
- oracle consulting (3)
- PostgreSQL (1)
- Quantum Computing (1)
- Quickbooks (1)
- SEO (1)
- Software Development (33)
- Systems Automation (2)
- Tech (3)
- Technology (51)
- UI (13)
- Uncategorized (8)
- UX (9)
- VSTO (1)
- Web Development (1)
- Windows (9)
- wordpress (1)